From Code to Runtime: The Entire Cloud Security Horizon Through a Single Lens 

Security Lens is GS Neotek's next-generation CSMP, centrally managing six key security pillars—CSPM, CWPP, CIEM, DSPM, Code Security, and Compliance—from a unified console.

Engineered with domestic regulatory compliance as a default standard and empowered by AI-driven operational automation, it seamlessly unifies the entire security lifecycle. 


Six Key Security Domains 

Eliminating security blind spots caused by fragmented tools. 

01

Cloud Security Posture Management (CSPM) 

Automated assessment against global security policy baselines 

02

Cloud Workload Protection Platform (CWPP) 

Behavior-based threat detection 

03

Cloud Infrastructure Entitlement Management (CIEM) 

Identification of permission anomalies and automated enforcement of least privilege 

04

Data Security Posture Management (DSPM) 

Sensitive data discovery and access permission visibility 

05

Code Security: Shift-Left 

Intercepting supply chain threats early at the code stage 

06

Security Information & Event Management (SIEM) 

Centralized log & event ingestion with real-time anomaly detection and response 

Key Features 

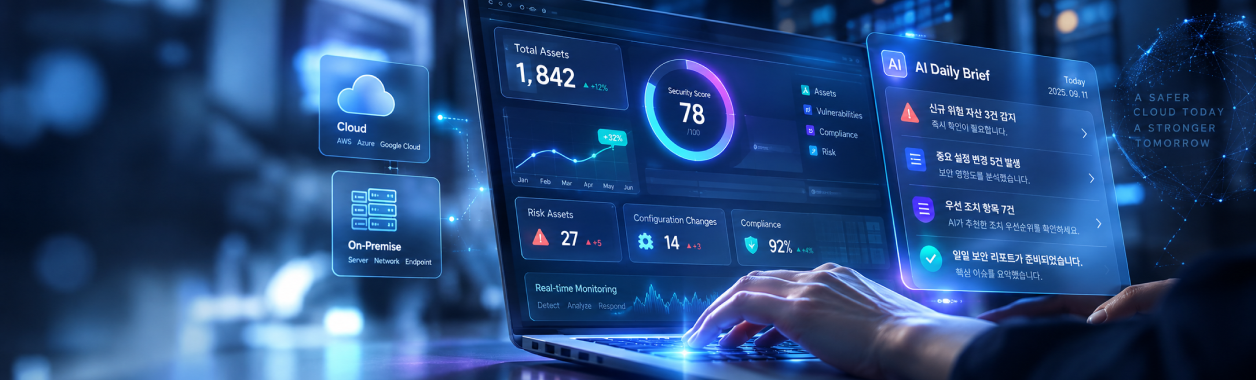
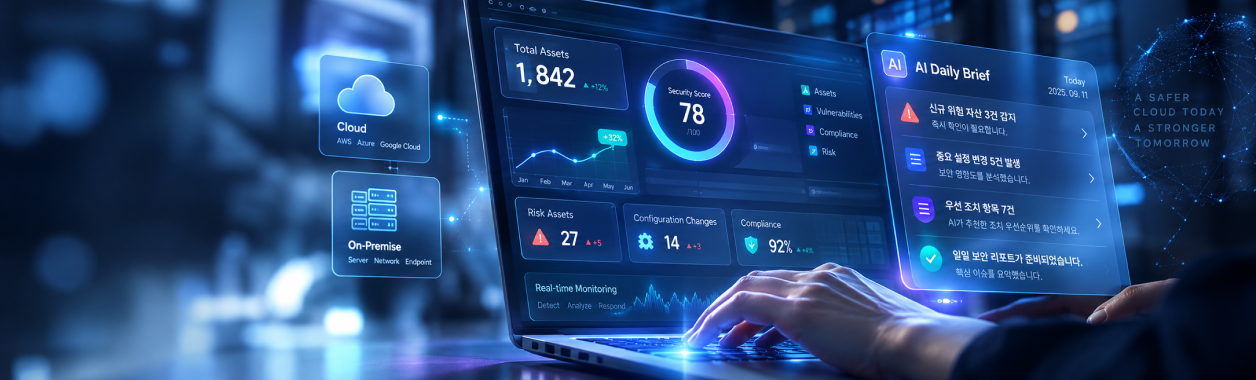
Enterprise-Wide Security & Asset Unified Visibility 

  • Integrated Security Scoring — Quantifies overall security posture, visualizing current status and improvement trends at a glance
  • Real-Time Risk Tracking — Instantly detects new findings, vulnerability spikes, and asset modifications
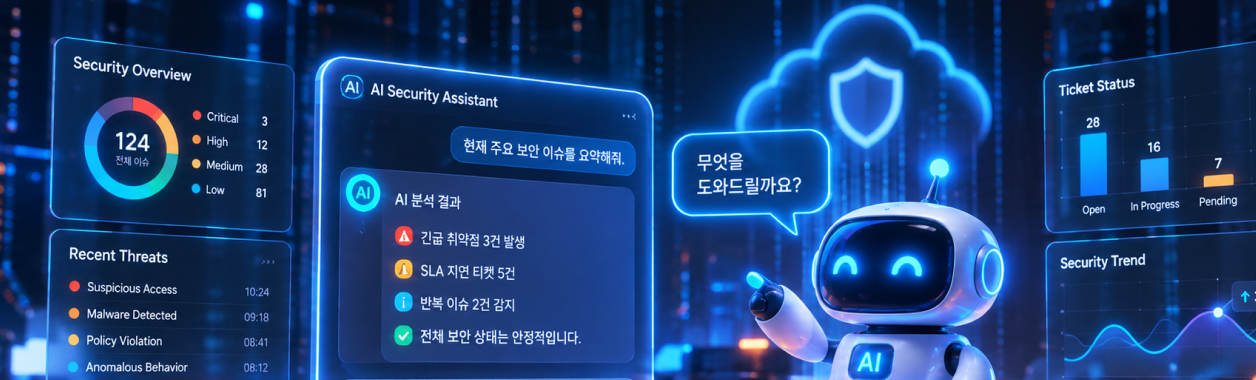
  • Daily AI Briefing — Delivers concise summaries of critical issues and recommended remediation priorities

Relationship & Attack Path Analysis 

  • Asset Topology Mapping — Visualizes relationships among assets including VPCs, Subnets, Security Groups, EC2, and S3 in graph views
  • Attack Path Visualization — Analyzes potential attack trajectories from internet-facing assets to core internal assets
  • Ontology-Based Asset Discovery — Automatically aggregates and classifies all cloud and on-premises assets

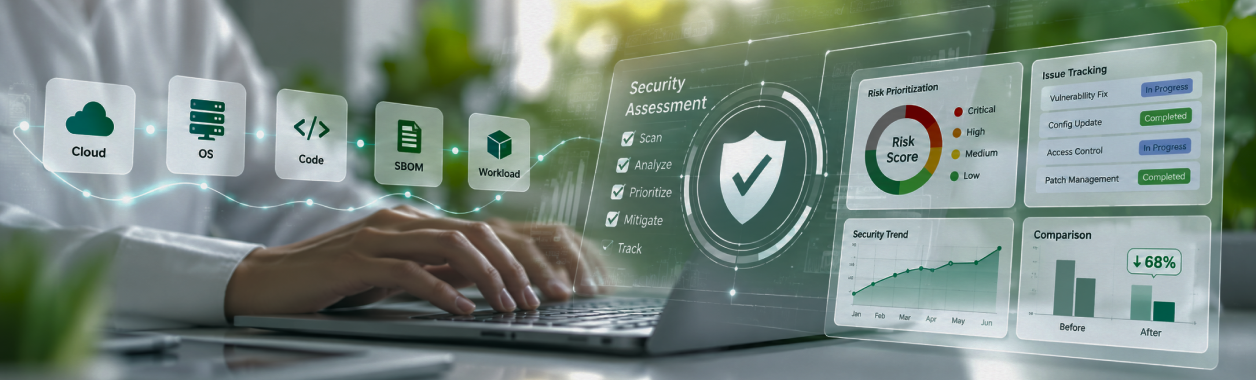
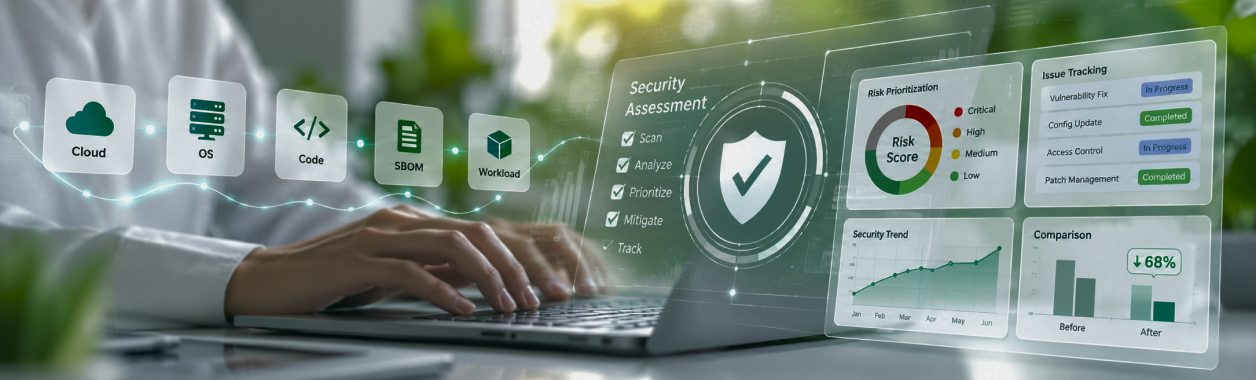
Integrated Vulnerability Assessment & Remediation History 

  • Unified Vulnerability Assessment — Consolidates assessment findings across Cloud, OS, Code, SBOM, and Workload into a single pane
  • Risk-Based Prioritization — Automatically identifies priority remediation targets based on severity, asset criticality, and exposure
  • Ticket-Based Audit Trail — Converts remediation workflows into trackable tickets to monitor progress and recurrence risks against past baselines

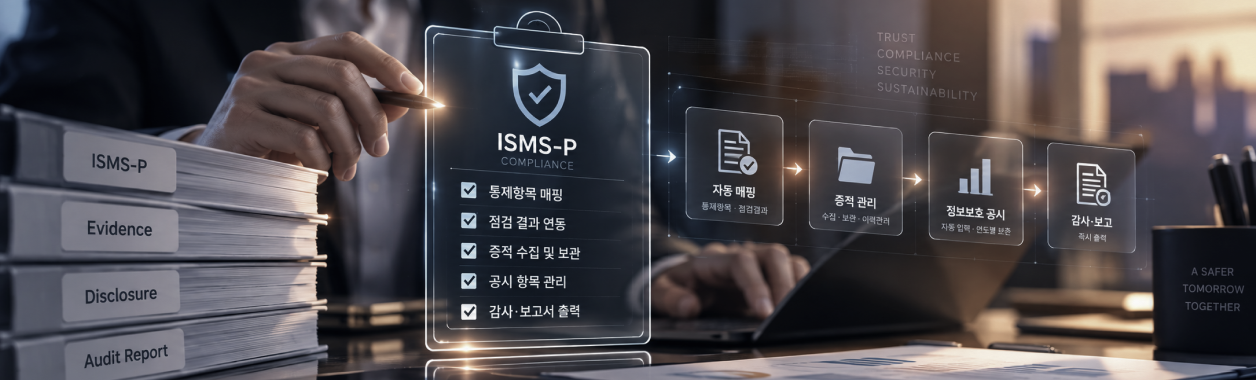
Compliance & Audit Operations 

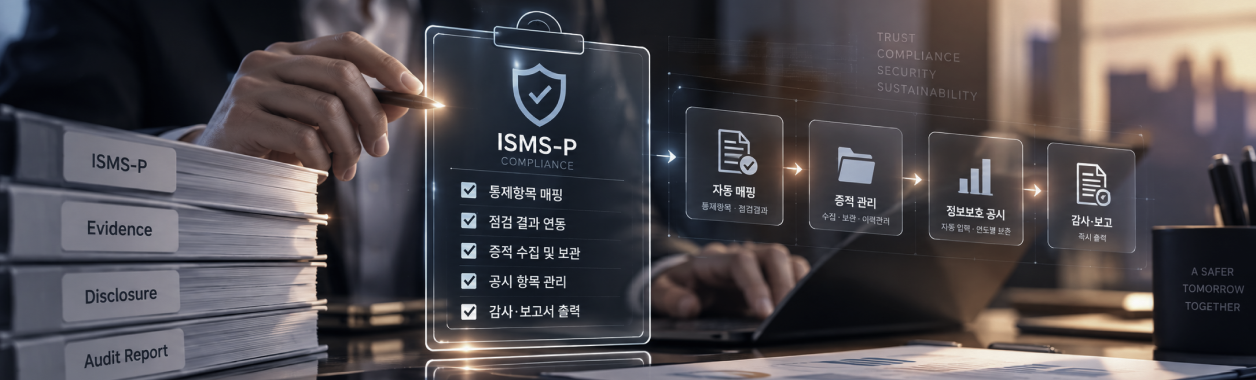
  • Unified Compliance Management — Unifies control items, evidence, and remediation statuses to significantly reduce audit prep time
  • SLA & Report Governance — Tracks remediation deadlines, violations, and completion statuses with instant export of audit-ready reports
  • AI-Powered Automation — Automates evidence verification, compliance status tracking, and documentation data entry

AI-Powered Security Operations Support

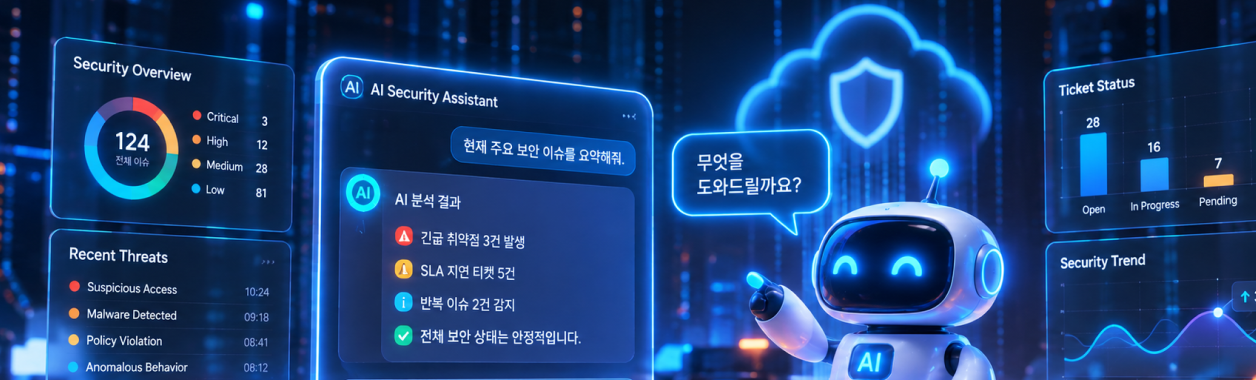
  • AI Security Posture Summaries — Condenses assessment results and complex telemetry for immediate executive visibility
  • Natural Language Queries — Query security scores, vulnerabilities, tickets, and compliance statuses via an interactive chatbot
  • Priority Action Recommendations — Suggests immediate action items based on risk severity, affected assets, and remediation status
  • Trend & Risk Analytics — Pinpoints operational bottlenecks by analyzing recurring issues, SLA delays, and systemic changes

Expected Benefits 

Real-time visibility into all cloud and on-premises assets within a single dashboard

  • Quantitative tracking of current posture and progress via security scores
  • Elimination of response gaps through instantaneous detection of risky assets and configuration drift
  • Automated daily delivery of critical issues and remediation priorities via AI Daily Brief

Proactive identification of potential attack paths from internet-exposed assets to critical infrastructure 

  • Comprehensive threat flow visualization using asset topologies to uncover multi-stage attack vectors
  • Maximum risk reduction with minimal effort by focusing remediation on strategic Choke Points
  • Continuous attack surface management across IAM, sensitive data, and container resources

Unified, single-framework assessment across Cloud, OS, Code, SBOM, and Workload 

  • Rapid response within the golden hour for critical vulnerabilities via automated risk prioritization
  • Permanent ticket-based remediation audit trails to verify issue resolution and prevent recurrence
  • Quantitative validation of security posture improvements by comparing historical assessment results

Reduced audit preparation time through automated mapping between ISMS-P control requirements and assessment findings 

  • Automated evidence collection and archiving, preventing documentation loss during staff turnover
  • Simplified public information security disclosure via automated data entry and multi-year record retention
  • Minimized compliance response costs and timelines through instant export of audit-ready documentation

Rapid identification of key issues through AI-driven summarization and analysis of complex security telemetry 

  • Instant access to security scores, vulnerabilities, and tickets via natural language chatbot queries
  • Continuous operational refinement through automated analysis of recurring bottlenecks, SLA delays, and major changes
  • Establishment of an effective security operations framework empowered by AI, even with lean security teams